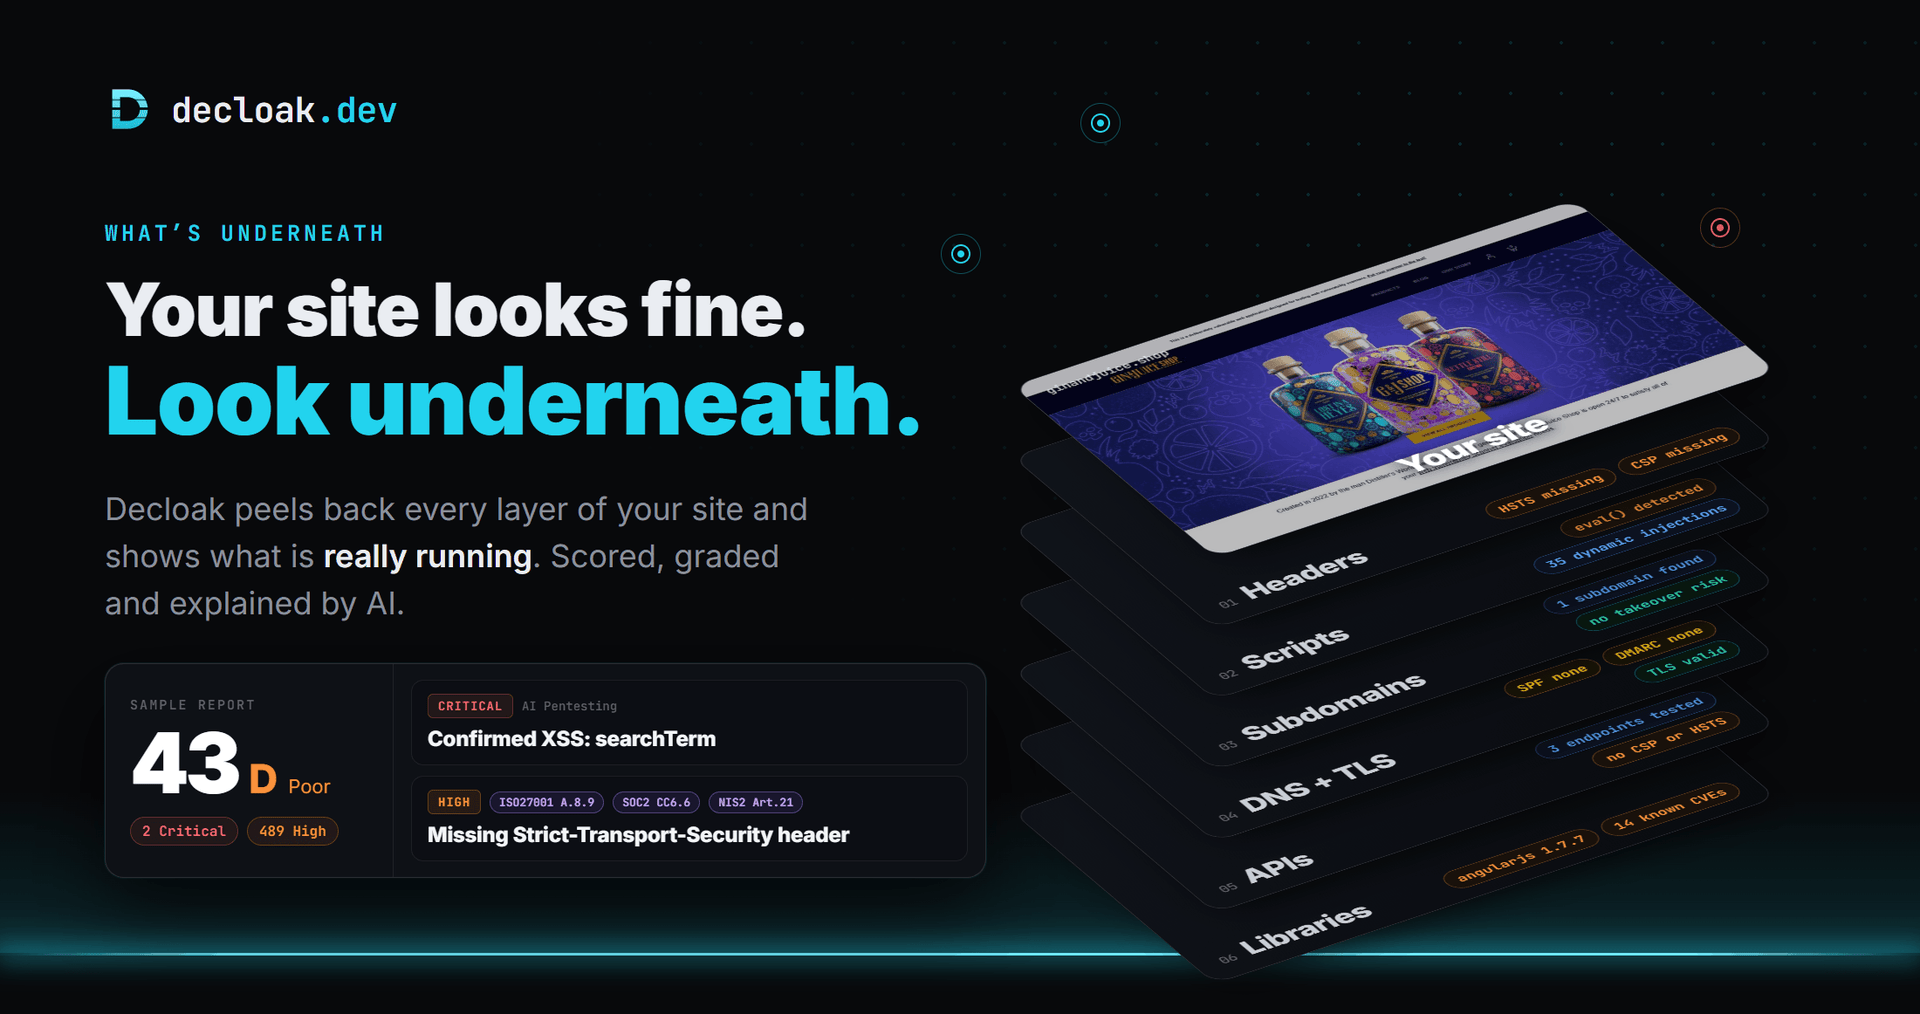

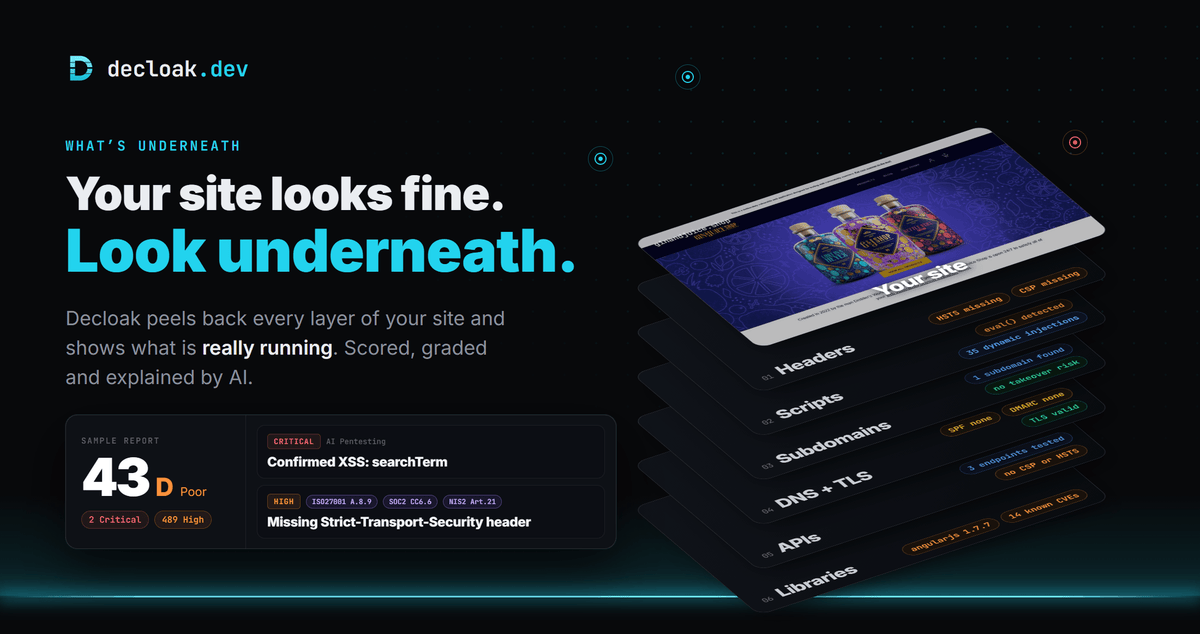
Every web application, client site, and modern API has hidden attack surfaces. From forgotten staging endpoints and exposed environment variables to outdated JavaScript dependencies and unauthenticated database queries, modern web development moves faster than traditional security teams can monitor. Decloak bridges that gap by delivering automated web security intelligence, combining ultra-fast surface scanning with autonomous AI-driven penetration testing.
Rather than drowning development teams in noisy alert logs or demanding five-figure annual enterprise contracts, Decloak inspects your domains and IP addresses in approximately 15 seconds, assigns a clear A–F security grade, and launches an autonomous AI agent that investigates up to 200 pages deep to verify real exploitable vulnerabilities.
What Is Decloak?
Decloak is a modern web application security testing and dynamic application security testing (DAST) platform designed to catch vulnerabilities before malicious actors exploit them. Unlike legacy vulnerability scanners that rely solely on surface header checks or static signatures, Decloak operates as an intelligent automated security analyst.
With more than 65 built-in web security checks, Decloak uncovers exposed API keys, source code leaks, vulnerable third-party libraries, and platform-specific misconfigurations. It doesn’t stop at theoretical warnings: Decloak actively validates threats in a sandboxed environment and maps every finding directly to global compliance standards, making enterprise-grade security accessible to developers, agencies, and growing businesses.
Why Choose Decloak Over Traditional Security Scanners?
Traditional website vulnerability scanners often suffer from two major flaws: they are either too shallow—reporting only generic SSL and HTTP header warnings—or too noisy, producing endless false positives that waste valuable engineering hours. Decloak redefines automated web security with several key advantages:
- Sub-15-Second Intelligence: Get an immediate, actionable snapshot of any website or IP address’s security posture with zero initial configuration.
- Autonomous Deep-Surface Investigation: An AI agent crawls up to 200 interconnected pages, systematically discovering hidden routes, neglected forms, and undocumented parameters.
- Active Exploit Verification: Instead of guessing whether a vulnerability exists, Decloak validates real exploitability using trusted, sandboxed security tools like sqlmap, ffuf, nuclei, and jwt_tool.
- Native Support for Modern Vibe-Coding Stacks: Automatically audits applications built on modern AI and low-code platforms including Lovable, Supabase, and Base44 for misconfigured Row-Level Security (RLS) policies and exposed service keys.
- Built-In Regulatory Alignment: Connects technical findings directly to SOC 2, ISO 27001, NIS2, and DORA control frameworks, dramatically shortening audit preparation cycles.
- Transparent Lifetime Economics: Replaces recurring monthly software subscriptions with a predictable one-time investment through Dealify.
Complete Feature Breakdown
Decloak consolidates multiple specialized penetration testing and posture-management utilities into a unified, user-friendly interface.

Rapid Security Scanning & A–F Grading
Type in any target domain or IP address and Decloak delivers a comprehensive security baseline in approximately 15 seconds. The platform calculates an intuitive A–F letter grade based on overall posture, highlighting urgent vulnerabilities, misconfigured HTTP headers, DNS anomalies, and SSL/TLS configuration weaknesses so you immediately know where you stand.
Autonomous AI Agent for Deep Surface Investigation
Shallow scanners only inspect the homepage. Decloak deploys an autonomous AI agent capable of investigating up to 200 pages across your target site. The AI follows potential threat leads, analyzes page structures, identifies dynamic form submissions, and discovers hidden endpoints that standard automated scripts overlook.
Sandboxed Active Penetration Testing (DAST)
Alert fatigue happens when scanners report theoretical issues that pose no real risk. Decloak incorporates integrated active penetration testing utilities—including sqlmap, ffuf, nuclei, and jwt_tool—within an isolated, sandboxed execution environment. This confirms whether discovered injection points, directory listings, or broken token implementations can actually be exploited by an attacker.
Source Map Analysis & Exposed Secret Detection
Modern frontend build pipelines frequently bundle sensitive data or inadvertently publish JavaScript source maps to production. Decloak reconstructs source trees from exposed .map files, inspecting raw code for leaked API keys, database credentials, internal endpoints, and third-party SaaS tokens before attackers can reverse engineer them.
Modern API Security Auditing
Modern web applications rely heavily on APIs. Decloak automatically identifies and tests REST, GraphQL, and SOAP endpoints across your infrastructure. The platform evaluates authentication barriers, checks for Broken Object Level Authorization (BOLA), and checks endpoint input sanitation to defend against data exfiltration.
Vibe-Coding & AI Platform Protection
As rapid development platforms like Lovable, Supabase, and Base44 become ubiquitous, developers frequently ship code with default administrative settings or overlooked database policies. Decloak includes specialized platform detectors that audit Supabase Row-Level Security (RLS) configurations, detect exposed service roles, and secure rapid-built web applications before launch.
Built-In Compliance Mapping & Audit-Ready Reports
Security without documentation slows down sales and compliance audits. Decloak automatically maps every detected finding to relevant security frameworks, including SOC 2, ISO 27001, NIS2, and DORA. When audits arrive, export comprehensive, timestamped PDF evidence packages complete with risk scores, proof of vulnerability, and clear remediation guidance.
Expert Mode & Remediation Workflow
For security professionals who want granular control, Expert Mode unlocks custom testing payloads, configurable scan scopes, and advanced crawl parameters. Teams can track remediation status, assign specific findings to engineers, and execute one-click re-scans to verify fixes.
How Decloak Works: 4-Step Security Workflow
Implementing continuous web security doesn’t need to be complicated. Decloak streamlines the entire lifecycle into four straightforward steps:
- Target Ingestion & 15-Second Reconnaissance: Input your domain name or IP address. Decloak immediately conducts perimeter analysis, checks security headers, scans open ports, inspects SSL/TLS certificates, and outputs your initial A–F security grade.
- Autonomous Deep-Surface Crawl: The AI agent traverses your site up to 200 pages deep, mapping out APIs, dynamic scripts, authentication workflows, and potential injection vectors across the entire application.
- Sandboxed Exploit Verification: Discovered weaknesses are tested in real time using sandboxed penetration testing tools (sqlmap, nuclei, ffuf, jwt_tool) to verify whether each finding represents an active, exploitable vulnerability.
- Remediation Tracking & Compliance Export: Review prioritized findings with code-level fix recommendations. Assign items to your development team and export audit-ready PDF reports mapped directly to SOC 2, ISO 27001, NIS2, or DORA standards.
Who Should Use Decloak?
Decloak is engineered for anyone responsible for deploying, maintaining, or securing web assets who needs enterprise-grade security without enterprise complexity:
- AI App Builders & Vibe Coders: Validate applications built on Lovable, Supabase, or Base44 before going live. Ensure no API keys, client tokens, or misconfigured database policies slip into production.
- Startups & SaaS Founders: Secure your cloud application, protect customer data, and pass vendor security assessments required by enterprise buyers without hiring an in-house security team.
- Digital Agencies & Managed Service Providers (MSPs): Run automated security audits for client websites, deliver high-value white-labeled compliance reports, and create recurring security maintenance retainers.
- Security & Compliance Officers: Automate continuous vulnerability monitoring, eliminate manual evidence gathering for SOC 2 and ISO 27001, and verify that developers maintain rigorous security posture.
- Full-Stack Developers & DevOps Teams: Shift security left into your deployment workflow. Catch outdated JavaScript libraries, source map leaks, and vulnerable endpoints before release day.
Decloak Lifetime Deal Analysis: Value & Long-Term ROI
Traditional DAST tools, automated penetration testing software, and cloud compliance platforms typically charge between $99 and $400 per month—costs that quickly become prohibitive for solo developers, agencies managing dozens of websites, and early-stage startups.
The Decloak Lifetime Deal on Dealify starts at an entry point of just $49 (discounted from the standard $490 valuation, saving 90%). For a single, one-time investment, users secure ongoing access to 65+ automated security checks, autonomous AI investigations, active penetration testing, and compliance documentation.
Combined with Dealify’s 60-day money-back guarantee, buyers can test Decloak thoroughly across their entire web estate with zero financial risk. Whether you manage a single flagship SaaS or a fleet of client websites, Decloak provides immediate visibility, continuous peace of mind, and significant long-term savings.